

Outtake vs Bolster: 2026 comparison
Bolster is an AI-powered brand security platform. Outtake is next-generation digital risk protection, with detection that starts from what you own, investigation that reaches the campaign behind each threat, and API and MCP access.
Updated October 15, 2026
The short verdict
Outtake detects from a registry of everything you own, so a fake is caught even when it never uses your exact name. Recon Agent expands one alert into the campaign and accounts behind it, and takedowns are followed until they are confirmed down, with a 99.4% confirmation rate. A REST API, webhooks, and an MCP server let your team run Outtake from the tools it already uses.
Three reasons teams choose Outtake over Bolster
Detection that starts from what you own
The Entity Registry holds your brands, executives, locations, and products, with aliases and reference images. Agentic Search reads text, images, video, and audio, so an impersonation is found even when it never uses your exact name.
The campaign, not only the URL
Recon Agent and Threat Graph turn one alert into the wider network of domains, accounts, and ads behind it. Actor Tracing links posts to the accounts that run them, and proposed links are confirmed before they are added.
Run it from your AI tools
Pull alerts and file takedowns through the REST API and webhooks, or connect Outtake's MCP server to Claude and other AI tools. Read digests, check protected entities, and preview, file, and track takedowns in plain language.
What security leaders tell us

The market is three tiers. Keyword monitoring, then AI detection, then fully agentic. You're the agentic one. That's where we want to be.
The biggest value is not just triage. It is pattern recognition, reporting, and coordinated action.
We can finally see patterns across cases, not just chase one off complaints.
Anonymous comments from customers and evaluation calls. They do not refer to Bolster.
The quick comparison
Next-generation digital risk protection. Finds, investigates, and dismantles impersonation, fraud, and data leaks across 45+ surfaces.
Describes itself as an AI-powered brand security platform that combines AI detection with expert threat hunting.
Brands, executives, locations, and products across 45+ surfaces, including social platforms, domains, marketplaces, app stores, ad networks, messaging channels, and the dark web.
Lists websites, domains, social media, marketplaces, paid ads, mobile apps, email abuse, deepfakes, and the dark web.
Starts from an Entity Registry of your brands, executives, locations, and products. Agentic Search uses entity detection instead of keyword lists, and an AI check keeps the relevant results.
AI detection reviewed by Bolster's threat hunters. Also offers CheckPhish, a free scanner for suspicious URLs.
Threat Graph and Recon Agent expand one alert into the wider campaign. Actor Tracing links a post to the accounts behind it, and proposed links are confirmed before they are added.
Announced Signals, an intelligence capability, in October 2025.
Takedowns have a 99.4% confirmation rate. Outtake follows up with providers and re-reports items that come back.
Lists hosting provider and registrar integrations for removal, including AWS, Cloudflare, GoDaddy, Namecheap, Bluehost, and Tucows.
Executives sit in the Entity Registry with names, aliases, and reference photos. Detection covers deepfakes, cloned voices, impersonated profiles, and doxxing.
Lists deepfakes among the threat types it monitors.
MCP server for Claude and other MCP clients: digests, protected entities, URL submissions, takedown preview and filing, and confirmation tracking.
No MCP server is listed on Bolster's integrations page as of October 18, 2026.
REST API, webhooks when a workflow changes, digests by email, Slack, or Teams, and hand-offs to your SIEM, ServiceNow, or Jira.
SIEM, SOAR, threat intelligence, collaboration, email, and single sign-on integrations, including Splunk, Microsoft Sentinel, Cortex XSOAR, ThreatQ, Slack, Microsoft Teams, Jira, and Okta.
The Bolster column summarizes Bolster AI's published materials as of October 18, 2026. It does not include buyer feedback.
Run Outtake from your AI tools
Outtake has an MCP server. Connect it to Claude or another MCP client and work your digital risk program in plain language, from the latest digest to a filed takedown.
- Ask what changed this week and get the digest your team reads, with the alerts behind it
- List the entities you protect and check where they are being abused
- Submit a suspicious URL for review and enforcement
- Preview a takedown, file it, and track delivery and platform confirmations
Access is scoped to the Outtake profile you choose when connecting and to your own permissions on it.
- get_latest_digest
- list_entities
- submit_manual_report
- validate_alert_takedown
- submit_alert_takedown
- get_alert_report_communications
Why teams choose Outtake over Bolster
Where Outtake is stronger
- Detection anchored to your own entities, so a fake is caught even when it never uses your exact name
- Recon Agent and Actor Tracing turn one alert into the campaign and accounts behind it
- Takedowns have a 99.4% confirmation rate, and returning items are re-reported
- A REST API, webhooks, and an MCP server put alerts and takedowns in the tools your team already uses
- The platform handles 90% of cases on its own, with 96% true positive accuracy over the last 90 days
Outtake is the right fit if
- Fakes that never use your exact name are slipping through
- You need the campaign and operators behind a threat, not only the URL
- You want to work alerts and takedowns from your own tools or AI assistants
- Executives need protection from deepfakes, cloned voices, and impersonated profiles
How Outtake works
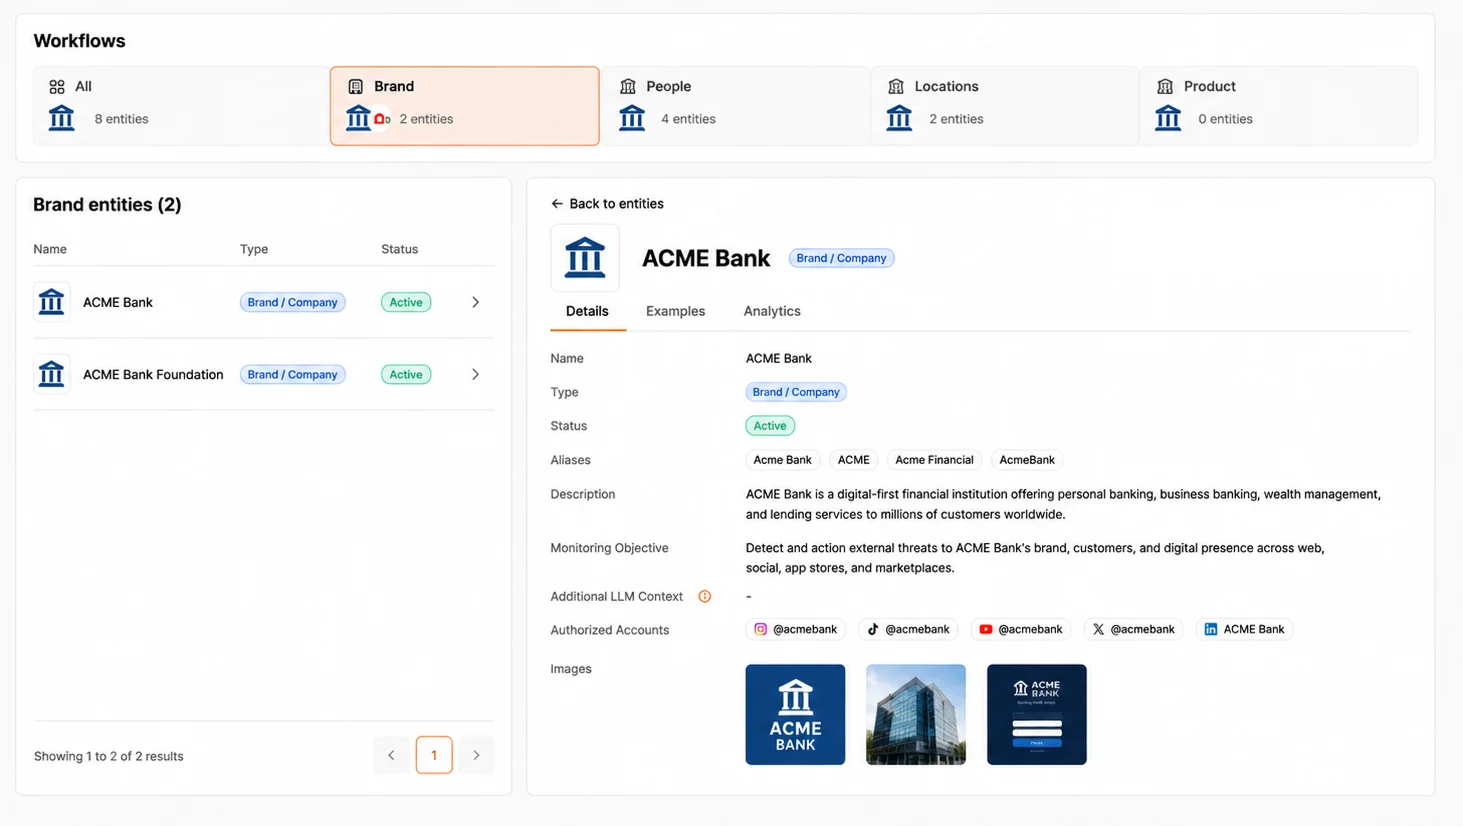
Outtake maps every entity linked to your organization: brands, executives, locations, and products. It separates what is authorized from what is not, so a fake is easy to spot even when it never uses your exact name.
Monitors your full digital footprint with entity detection instead of keyword lists, across 45+ surfaces including the public web and monitored messaging channels. It understands context, so it catches what keyword tools miss.
Keeps context on every entity, suspicious variant, fraudulent asset, adversary, and takedown it has seen. New threats triage against that history instead of starting cold.
Recon Agent turns one alert into the full campaign behind it. Actor Tracing connects the accounts, domains, and infrastructure to the operator running it, and proposed links are confirmed before they are added.
Routes each threat down the right response path and learns from every outcome. Guardrails decide what runs on its own and what waits for your team, and takedown status stays visible until an item is confirmed down.
Results teams see with Outtake
true positive accuracy, so your team only sees threats that matter
Outtake platform, last 90 days
faster takedowns than the previous provider, with threat reviews 3x faster
AppLovin case study
of cases handled by the platform on its own, with people stepping in at the moment of action
Outtake platform
Frequently asked questions
Is Outtake better than Bolster?
For digital risk protection across brands, executives, locations, and products, Outtake is the stronger fit. Detection starts from your Entity Registry, Recon Agent expands one alert into the campaign behind it, and takedowns have a 99.4% confirmation rate.
What is the difference between Outtake and Bolster?
Outtake starts from a registry of your entities and uses AI agents to detect, investigate, and dismantle threats across 45+ surfaces. Bolster describes itself as an AI-powered brand security platform that pairs AI detection with expert threat hunting.
Can Outtake replace Bolster?
For phishing domains, brand and executive impersonation, social, marketplace, and ad fraud, and takedowns, yes. During evaluation, list any Bolster integrations your team depends on and confirm the Outtake equivalent.
Does Outtake have an MCP server?
Yes. Connect Outtake to Claude or another MCP client to read digests, check protected entities, submit suspicious URLs, preview and file takedowns, and track platform confirmations. Access is limited to the profile you choose and your own permissions.
How does Outtake confirm a takedown?
Outtake reads provider replies, follows up, and re-checks until an item is confirmed down, then re-reports items that come back. The 99.4% rate counts alerts taken down out of reports submitted, with removal confirmed through remediation-case resolution.
More Outtake comparisons
Sources
- Bolster AI: Homepage
- Bolster AI: Integrations
- Bolster AI: CheckPhish
- Outtake: Platform
- Outtake: Brand Protection
- Outtake MCP server listing
Product names are trademarks of their owners. Competitor information reflects public materials as of October 15, 2026.