

Outtake vs Doppel: 2026 comparison
Both platforms detect and take down impersonation and fraud. Security teams that evaluated Outtake against Doppel kept describing the same gaps. Here is what they told us, and how Outtake closes them.
Updated October 15, 2026
The short verdict
Teams that compared Outtake with Doppel told us about impersonations Doppel missed, alerts their staff still checked by hand, and takedowns they could not trace. Outtake starts detection from a registry of what you own, so a fake is found even when it never uses your name. The platform handles 90% of cases on its own and reports every takedown step until the item is confirmed down.
What teams told us about Doppel

Lookalike domains went undetected
Impersonating domains with live mail records were missed and not taken down, and one kept coming back. That gap is what started their Outtake evaluation.
No name, no detection
A semi-viral video about the firm used a screen recording of its team page and never mentioned the firm by name. Doppel did not catch it.
Cross-channel funnels slipped through
A fake ad that sent victims to a WhatsApp attorney impersonation went unflagged. Their bar for a replacement is "novel findings Doppel misses."
Triage stayed manual
Staff reviewed every alert Doppel marked as confirmed, and false positives still got through. Related alerts were linked by hand in outside tools.
Takedowns they could not trace
They could not tell whether a takedown was Doppel's work or their own, and named Outtake's step-by-step reporting as the difference. They do not want to "babysit" a vendor.
The same mistakes, a year later
They had given Doppel "consistent feedback for a year and still see the same mistakes," and found its AI summaries unhelpful. They rated Outtake better on many fronts.
Paraphrased from evaluation and customer calls, July to October 2026. Organizations are anonymized.
The quick comparison
Next-generation digital risk protection. Finds, investigates, and dismantles impersonation, fraud, and data leaks across 45+ surfaces.
Positions itself as social engineering defense, pairing brand protection with security awareness training and email security.
Starts from an Entity Registry of your brands, executives, locations, and products. Agentic Search uses entity detection instead of keyword lists, and an AI check keeps the relevant results.
Buyers described misses: lookalike domains with live mail records, a viral video that never named the firm, and a fake ad that led to a WhatsApp impersonation.
Adaptive Workflows route each threat to the right response path. The platform handles 90% of cases on its own, and your team steps in at the moment of action.
One security team still reviewed every alert Doppel marked as a confirmed positive, false positives still got through, and related alerts were linked by hand in outside tools.
Analysts start takedowns in one click. Outtake reads provider replies, follows up, and re-checks until an item is confirmed down, then re-reports items that come back.
One buyer could not tell which takedowns Doppel completed and which their own team did.
Executives sit in the Entity Registry with names, aliases, and reference photos, so Agentic Search can find impersonations that reuse a face or a team page.
One buyer rated Outtake's executive protection ahead of Doppel's, and rarely used the Doppel version they had.
REST API, webhooks when a workflow changes, digests by email, Slack, or Teams, and hand-offs to your SIEM, ServiceNow, or Jira.
One buyer said Doppel's Slack bot went unused, so takedowns had to be filed inside the platform.
The Doppel column summarizes Doppel's own positioning and what security teams told us in evaluation and customer calls between July and October 2026.
Why teams choose Outtake over Doppel
Where Outtake is stronger
- Detection anchored to your own entities, so a fake is caught even when it never uses your exact name
- Recon Agent and Actor Tracing turn one alert into the campaign and accounts behind it, with links confirmed before they are added
- The platform handles 90% of cases on its own, with 96% true positive accuracy over the last 90 days
- Follow-through after a report: provider replies are read, items are re-checked until confirmed down, and returning items are re-reported
Outtake is the right fit if
- Impersonations that never use your exact name are slipping through
- Your team still checks confirmed alerts by hand
- You need to see each takedown step and who completed it
- You want executive protection your team actually uses
How Outtake works
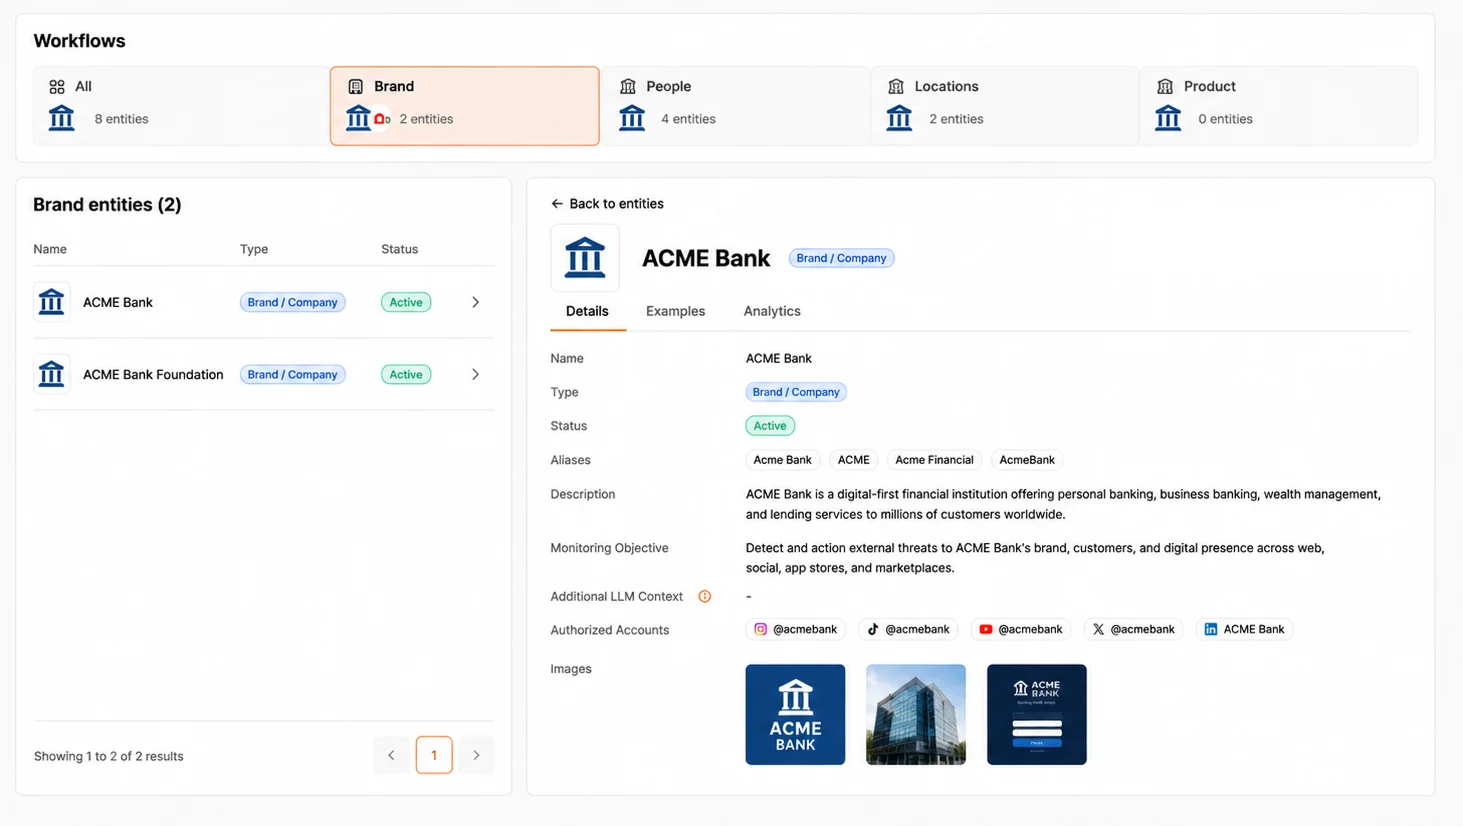
Outtake maps every entity linked to your organization: brands, executives, locations, and products. It separates what is authorized from what is not, so a fake is easy to spot even when it never uses your exact name.
Monitors your full digital footprint with entity detection instead of keyword lists, across 45+ surfaces including the public web and monitored messaging channels. It understands context, so it catches what keyword tools miss.
Keeps context on every entity, suspicious variant, fraudulent asset, adversary, and takedown it has seen. New threats triage against that history instead of starting cold.
Recon Agent turns one alert into the full campaign behind it. Actor Tracing connects the accounts, domains, and infrastructure to the operator running it, and proposed links are confirmed before they are added.
Routes each threat down the right response path and learns from every outcome. Guardrails decide what runs on its own and what waits for your team, and takedown status stays visible until an item is confirmed down.
Results teams see with Outtake
true positive accuracy, so your team only sees threats that matter
Outtake platform, last 90 days
faster takedowns than the previous provider, with threat reviews 3x faster
AppLovin case study
of cases handled by the platform on its own, with people stepping in at the moment of action
Outtake platform
Frequently asked questions
Is Outtake better than Doppel?
Several security teams that evaluated both told us Outtake was ahead on missed detections, manual triage, and takedown reporting. Outtake detects from a registry of your own entities, handles 90% of cases on its own, and reports each takedown step until the item is confirmed down.
What is the difference between Outtake and Doppel?
Outtake is built only for digital risk protection: an Entity Registry, Agentic Search, threat graphing with Recon Agent, and adaptive takedown workflows. Doppel positions itself as social engineering defense and pairs brand protection with training and email security.
Can Outtake replace Doppel?
For digital risk protection, yes: detection, investigation, takedowns, executive protection, and reporting. Outtake does not offer security awareness training or email security.
Does Outtake find impersonations that never use our name?
That is what the Entity Registry is for. Searches start from your brands, executives, aliases, descriptions, and reference images, so a fake can be found even when it never uses your exact name.
How does Outtake report takedowns?
Outtake reads provider replies, follows up, and re-checks until an item is confirmed down, then re-reports items that come back. Each step is visible, so your team knows what was done and by whom.
More Outtake comparisons
Sources
Product names are trademarks of their owners. Competitor information reflects public materials as of October 15, 2026.