Phishing and cloned login portals
Lookalike domains and cloned client portals, removed along with the hosting behind them.



Cloned login portals and fake investment platforms run as coordinated campaigns. Outtake's Next-Gen DRP maps the whole operation and takes down every connected asset
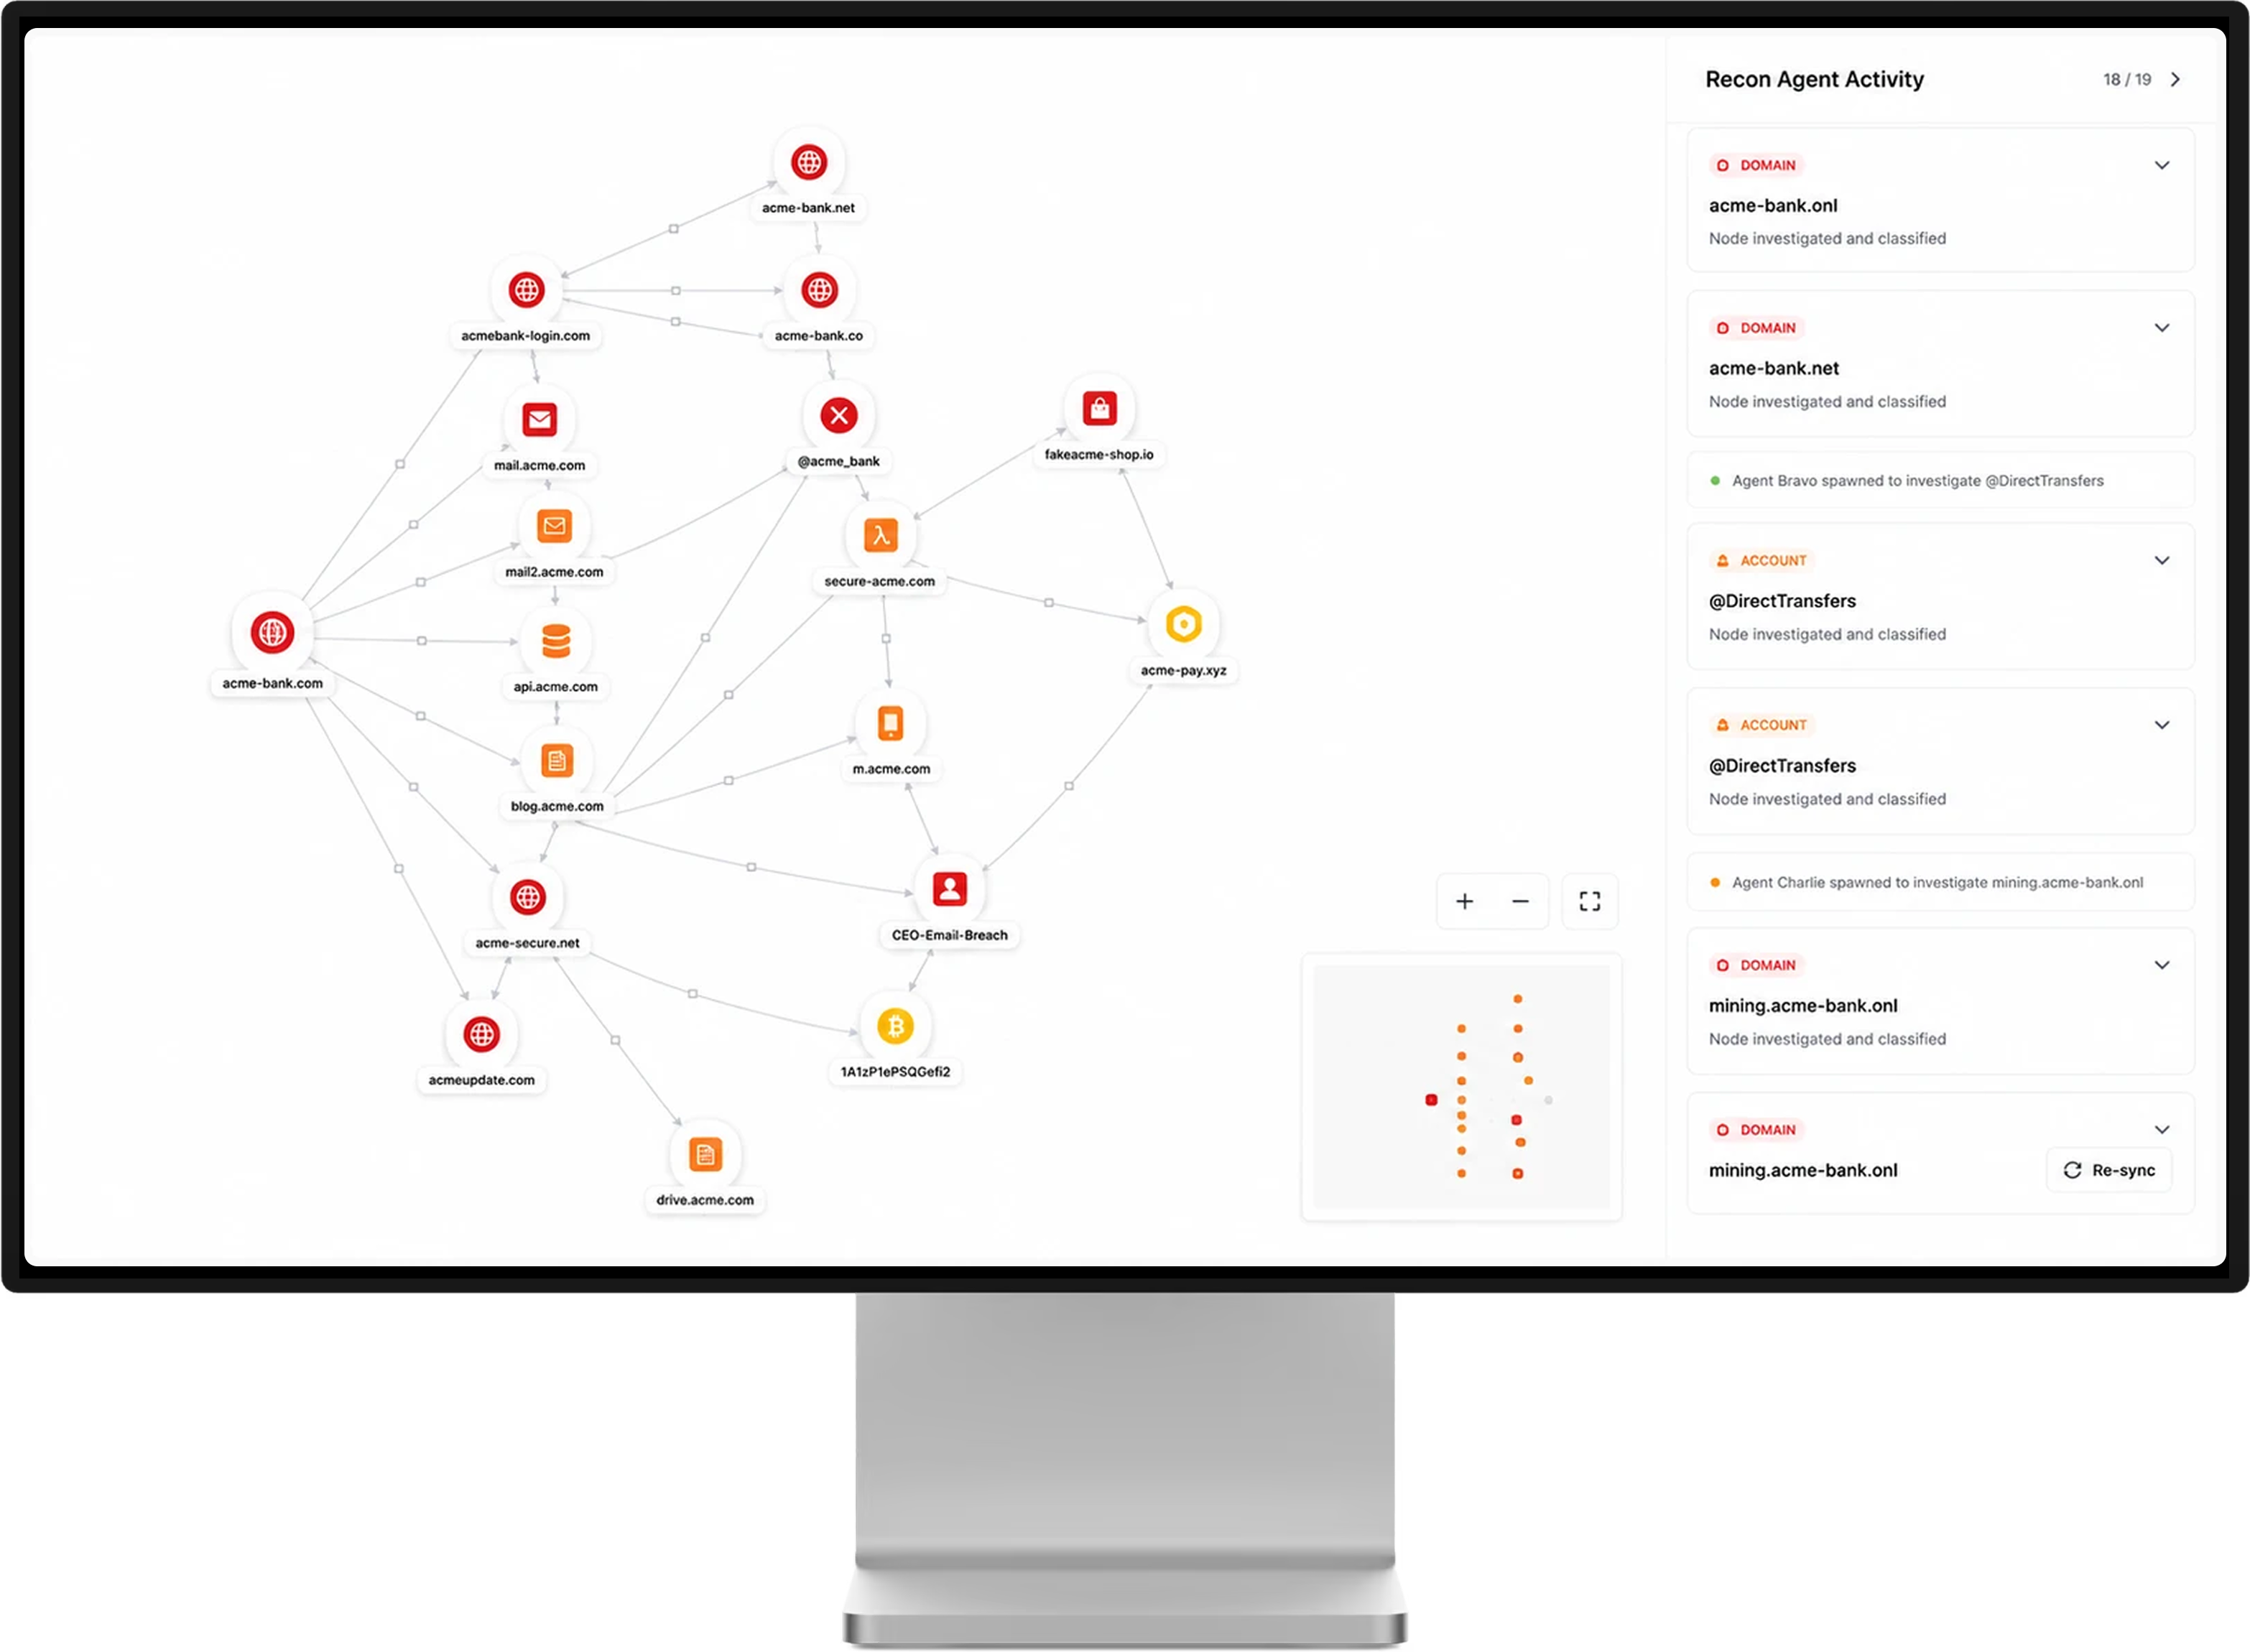
Next-Generation Digital Risk Protection finds and removes scams that impersonate a financial institution outside its network, including cloned login portals, fake trading platforms, advisor impersonation, fraudulent ads, and counterfeit apps. The Threat Graph links the domains, accounts, and wallets behind each scam so analysts can investigate the campaign and remove connected assets together in hours.









Scammers borrow a trusted institution's identity to capture credentials, redirect payments, and push fraudulent investments. Each convincing fake makes the next one easier to believe, and the assets below are built to work together.
Lookalike domains and cloned client portals, removed along with the hosting behind them.
Fraudulent trading portals and crypto schemes promoted through social profiles and messaging groups.
Fake profiles using the names and photos of your executives, advisors, brokers, and agents.
Paid placements that send customers into fraudulent schemes, caught by visual match.
Counterfeit mobile apps and fake support accounts waiting for customers who need help.
Leaked credentials and wallet infrastructure that tie separate scams back to one operator.
Legacy digital risk protection was built for a slower attacker. Those tools match keywords and hand each alert to an analyst, who files takedowns one URL at a time. Scammers stand up the replacement domain before that ticket closes.
Result: The visible asset comes down while the hosting, accounts, and sister domains behind it stay live.
Result: Analysts remove the connected assets together, including the infrastructure operators use to run the campaign.
Cloned login pages and fraudulent account alerts.
Scams that move fast across social and video platforms.
Fake advisors and cloned client portals.
Fake agents and fraudulent claims services.
Fraudulent loan offers and advance-fee schemes.
Fake exchanges and the wallet infrastructure behind them.
Register your brands, executives, advisors, domains, and apps once. Outtake uses that record to identify impersonations.
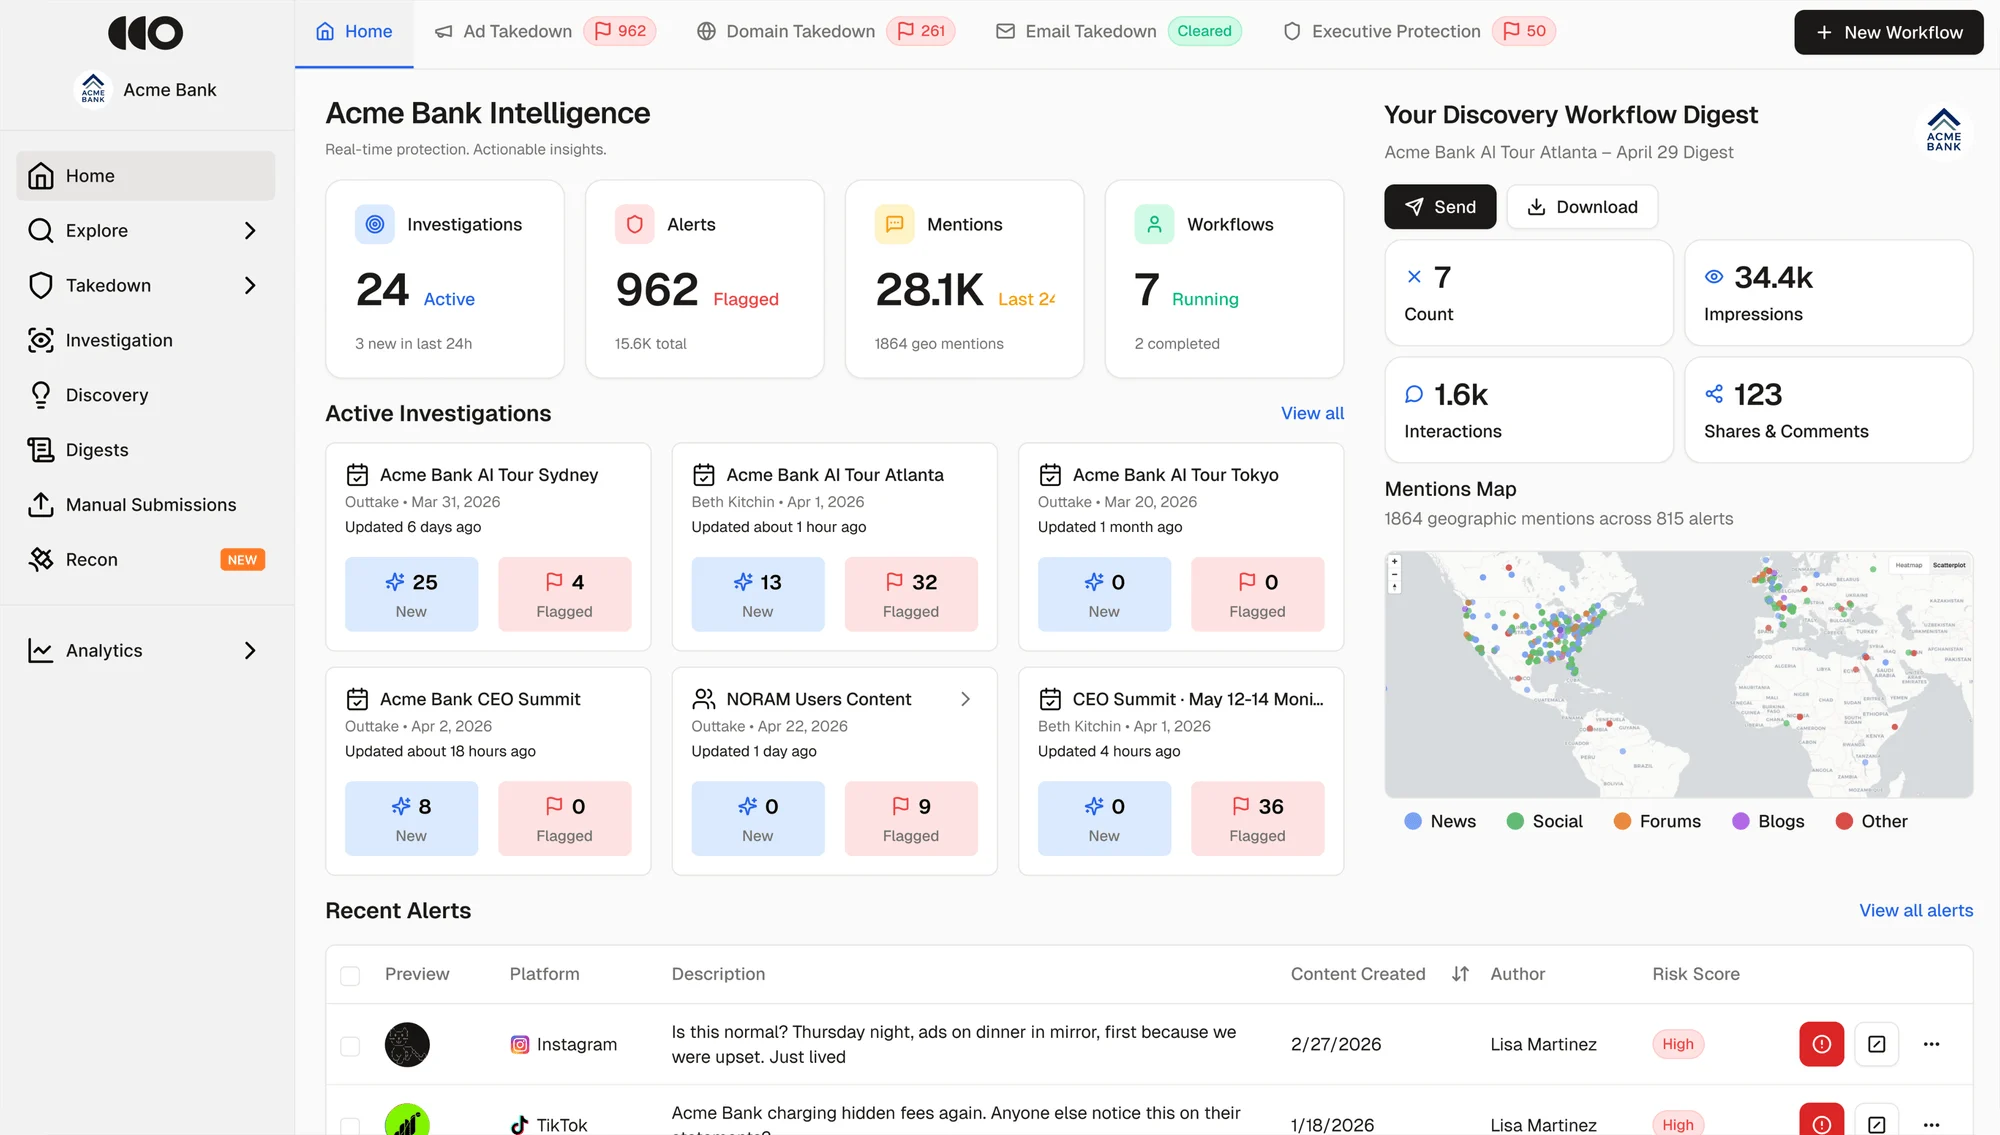
Agentic Search reads logos, layouts, images, video, and audio across monitored channels to distinguish brand mentions from active fraud campaigns. Recon Agent rescans every 16 minutes.

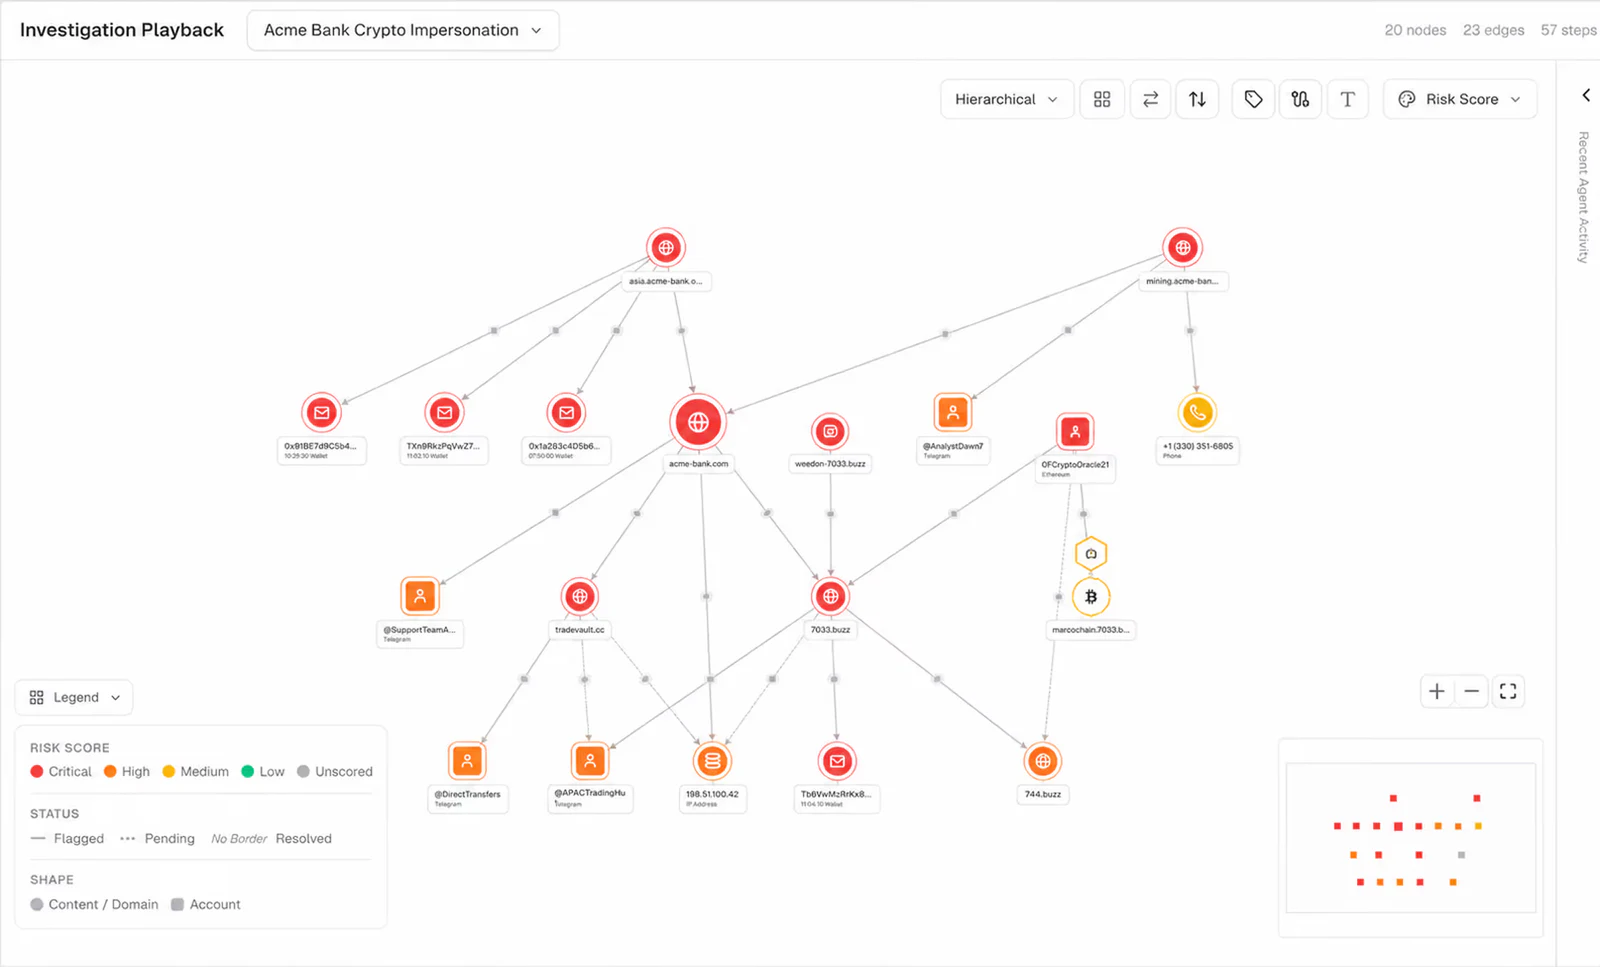
The Threat Graph links the spoofed domains, fake apps, ad accounts, chat groups, and wallets behind each scam, so your analysts can investigate the connected assets in one case.
Outtake sends takedown requests to the registrars, hosts, and platforms connected to a campaign in parallel. Removals take hours, with a 99.4% confirmation rate. Agents handle cases from discovery to removal without a queue, and analysts can track their progress.


“Outtake gave us full visibility into every platform our customers are using and the proof to show leadership we're catching threats before they ever have the chance to spread.”
“The 24 hour digest surfaced threats we missed on the feed of a different tool. We have been very happy with it.”
“You just did what I spent all day yesterday doing, in five minutes. I can't think of enough good adjectives about this.”
Aggregate performance for financial services customers as of August 26, 2026
Watch how Outtake investigates a malicious signal to find the fake trading platform, social profiles, messaging groups and payment infrastructure behind a pig butchering campaign.
Explore pig butchering defense

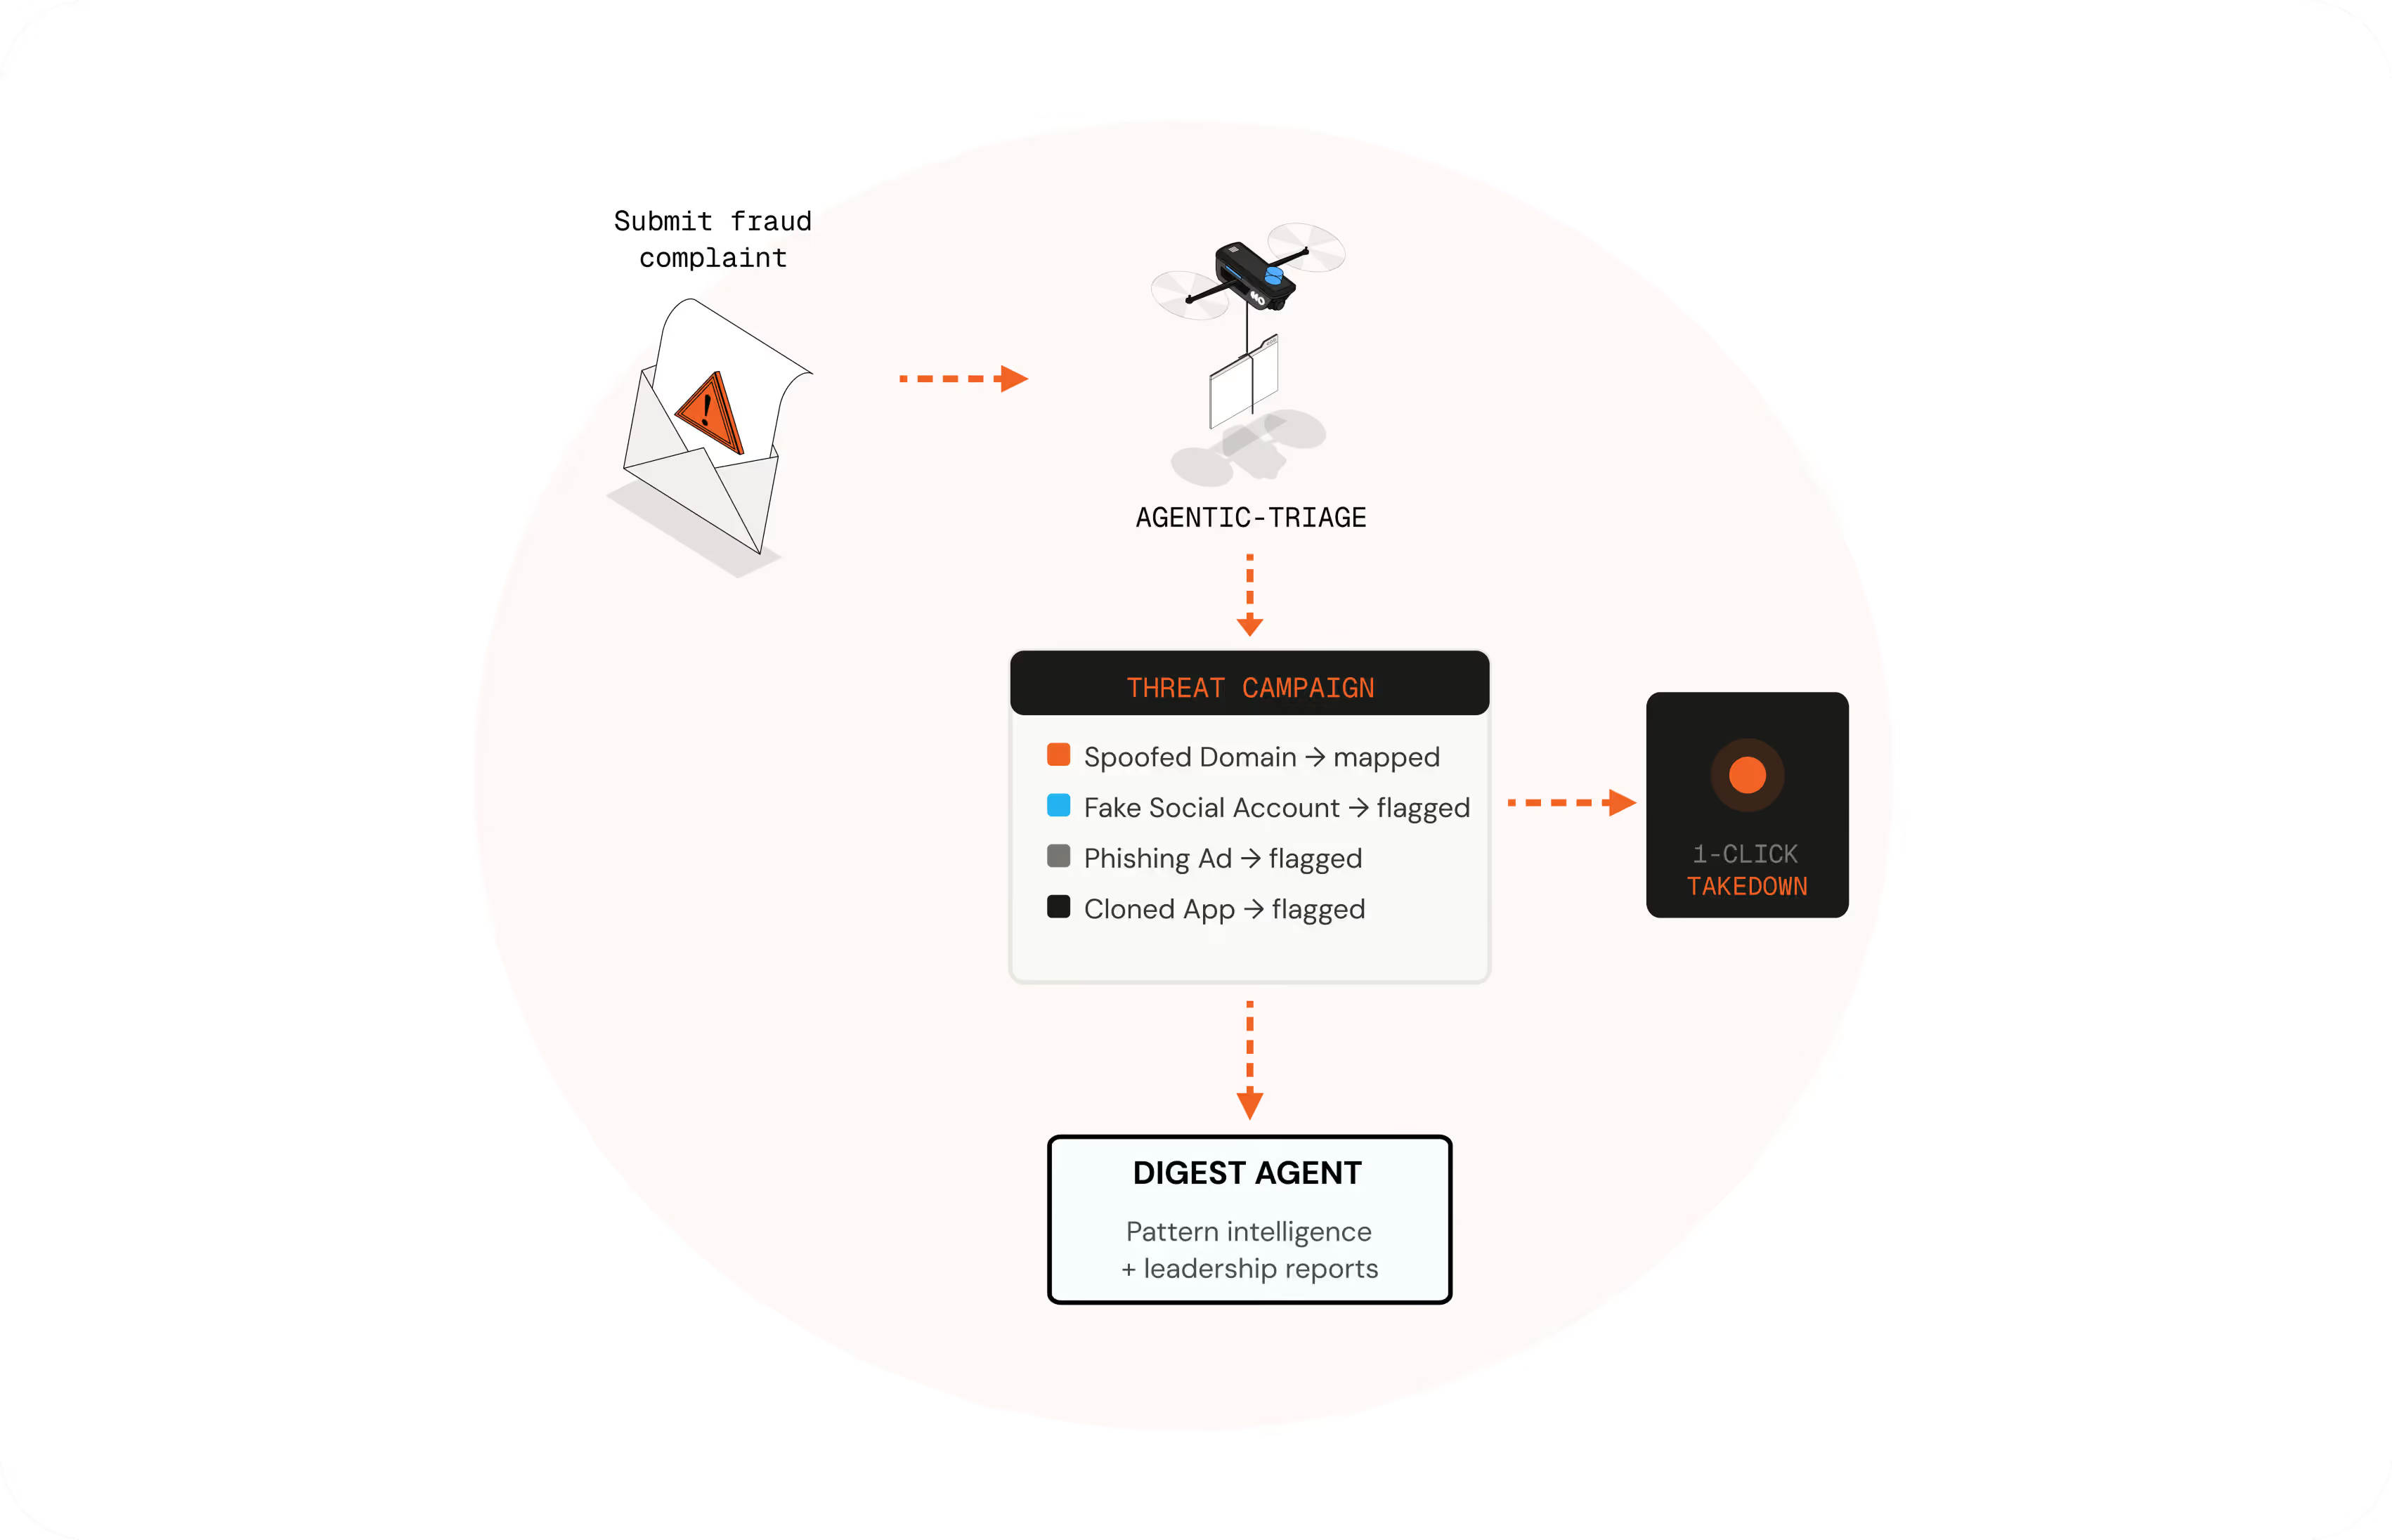
The hosting, sister domains, social accounts, redirect infrastructure, messaging groups, and wallets supporting the campaign may remain active. Outtake maps these connections so teams can act on them together.
Cloned login portals, fake investment and crypto platforms, executive and advisor impersonation, malicious ads, counterfeit apps, fake support channels, and related dark web infrastructure.
No. Agentic Search reads logos, layouts, images, video, audio, language, and context to distinguish ordinary mentions from active fraud.
Removals take hours in many cases. Outtake confirms 99.4% of takedowns, with more than 90% of social takedowns completed in under 24 hours.
The Threat Graph links domains, accounts, apps, ads, chat groups, and wallets in one investigation, then workflows coordinate action across the connected assets in parallel.
Outtake follows the signal from promotional content and impersonated profiles into messaging groups, fake trading platforms, payment infrastructure, and operator-linked wallets.
No. Outtake complements those controls by finding and removing external fraud infrastructure before it reaches transaction, complaint, chargeback, or escalation queues.
Major social networks, video platforms, messaging apps, app stores, search engines, paid ads, domains, marketplaces, and dark web sources.
Security, fraud, brand protection, legal, executive protection, and investigation teams use Outtake to share one connected view of external threats and coordinate response.